


Download the report
Click here
Now in its fourth year, the HSF Kramer Cyber Risk Survey draws on the views of general counsel and senior legal counsel across Australia's leading organisations to examine how legal leaders perceive, prepare for and respond to cyber risk.
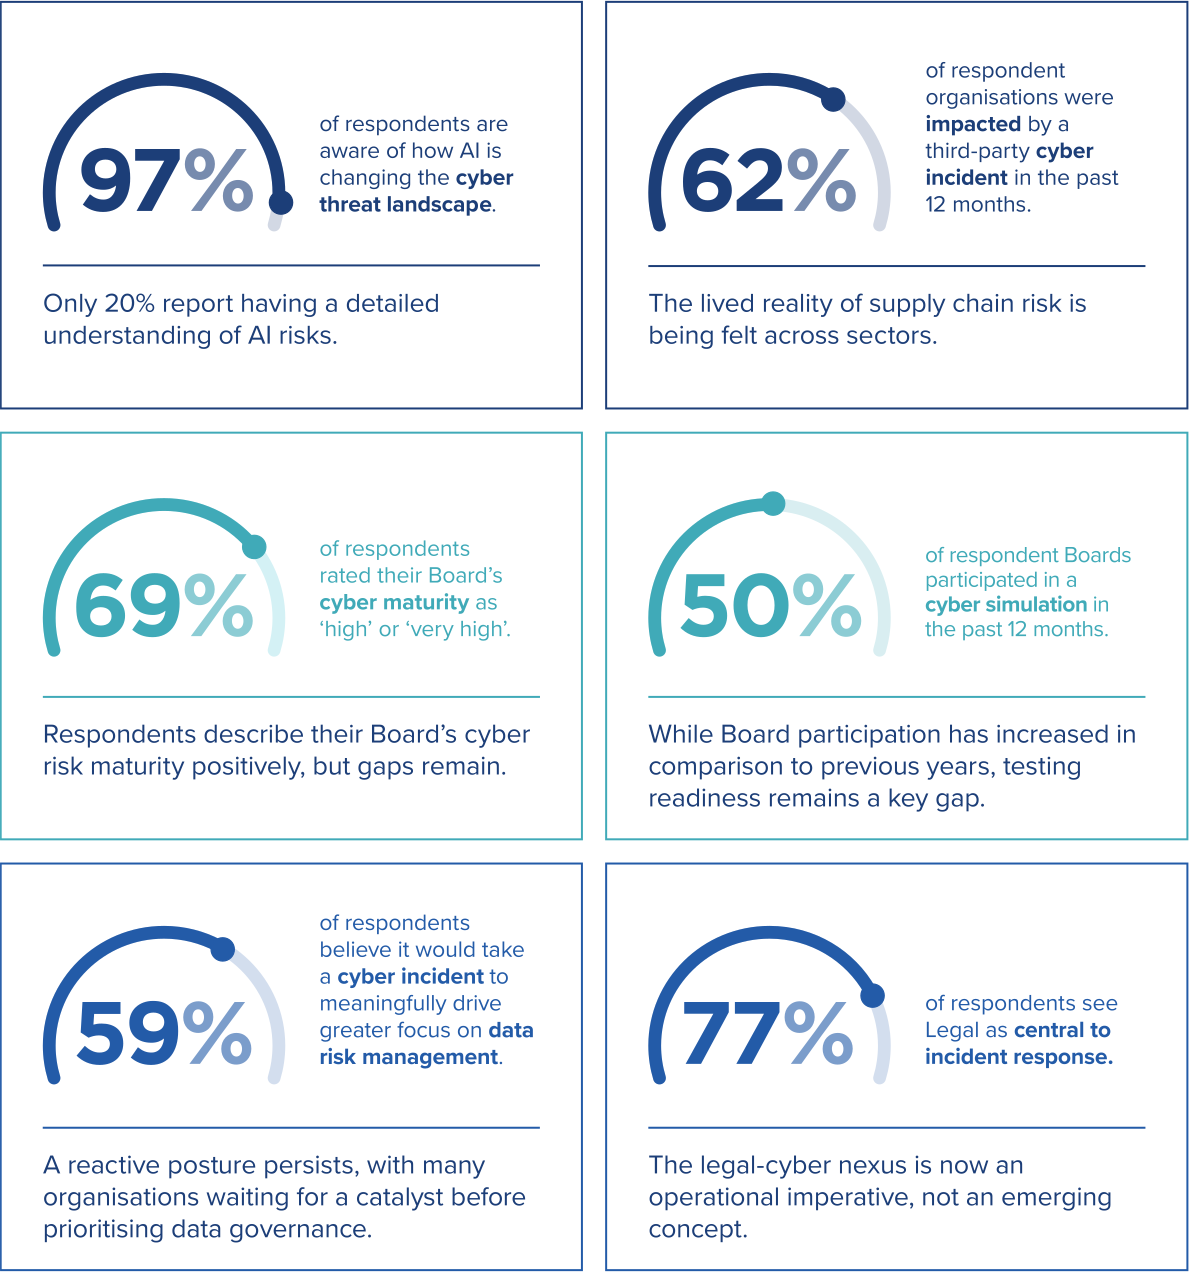
The defining story of 2026 is AI. 97% of respondents are aware of how AI is changing the threat landscape, yet only 20% report a detailed understanding of those risks.
Third-party risk remains the leading concern, with 62% experiencing a supply chain cyber incident in the past 12 months.
A reactive approach to governance persists, with 59% believing it would take a cyber incident to drive meaningful focus on data risk management.
Despite material improvements in board cyber maturity, significant gaps remain between awareness and readiness across data governance, people risk and incident preparedness.
Drawing on deep expertise across cyber incident response, regulatory compliance and data governance, this report offers a clear view of where Australian organisations stand today and what it will take to become genuinely cyber resilient.
The Report covers:
Cameron Whittfield
Partner, Cyber, Data and Emerging Technologies


Magdalena Blanch-de Wilt
Executive Counsel

|
AI as the key cyber riskthe emergence of AI-driven threat vectors and the challenge of AI risk in existing cyber frameworks |

|
The human element as a persistent vulnerabilityPeople-related risk ranks as top-three concern, yet remains absent from top investment priorities, revealing a disconnect between risk recognition and directed action |

|
Third-party risk entrenched at the topPersistent supply chain exposure, with ‘fourth-party’ risk visibility emerging as the dominant pain point |

|
Board maturity improving, but gaps remainIncreasing confidence in Board cyber maturity, yet simulation participation and ransom preparedness still fall short |

|
Data risk managementWhile most respondent organisations have taken steps to review data management practices in the past 12 months, 59% of respondents believe it would take a cyber incident to meaningfully drive greater focus on data risk management |

|
Legal teams as essential crisis respondersDeepening integration of legal functions into incident response, simulations and cyber incident response frameworks |
See how our global Cyber team can help you

Partner, Melbourne

Executive Counsel, Melbourne
The contents of this publication are for reference purposes only and may not be current as at the date of accessing this publication. They do not constitute legal advice and should not be relied upon as such. Specific legal advice about your specific circumstances should always be sought separately before taking any action based on this publication.
© Herbert Smith Freehills Kramer 2026
Receive timely insights and briefings from HSF Kramer, tailored to keep you informed and ahead
